
Banking Apps That Block Foreign IPs: The Traveller’s Workarounds
By  Ignas Simkus|Last updated: 22 July 2026|How we test
Nothing improves a trip like your own bank deciding you are a criminal. I spend close to half of each year outside Germany, so my banking apps live in permanent travel mode, and this guide is written from repeat offence. Blocked logins, frozen cards and vanished verification texts are all the same root problem: you moved, and your bank’s fraud model noticed. Every piece of it is preventable, mostly before you leave.
Article Summary
- Blocked login: a VPN server in your home country usually restores access
- Missing SMS codes: keep your home SIM active alongside the travel eSIM: dual SIM is the fix
- Frozen card: prevention is app-based travel notices and a backup card on a different network
- Best habit: test bank + VPN together once at home, before you need it in an airport
Why banks do this
Fraud models score every login and transaction, and geography is a heavy input: a login from an IP address in a country you have never banked from looks exactly like a stolen credential. Some banks step up verification; some, particularly smaller and regional ones, block foreign IP ranges outright. Behaviour varies wildly between banks and changes without notice, so treat any specific bank’s reputation, ours included, as a snapshot of reader and community reporting rather than policy: banks do not publish these rules, on purpose.
The reported pattern among big US banks, useful as expectation-setting rather than gospel: Bank of America and Wells Fargo are widely described as the hardest for international access, actively blocking shared VPN ranges (and sometimes whole foreign IP ranges); Chase sits in the middle, blocking shared IPs but generally tolerating a stable home-country connection; Citi’s app works from most countries (with SMS codes arriving slowly abroad, so switch to its authenticator first), and Capital One is repeatedly reported as the least aggressive about VPN connections. European and UK fintech-generation banks are broadly more travel-tolerant than the legacy names.
Fix one: look like you are at home
A VPN with a server in your home country gives the fraud model the input it wants: a familiar IP address in a familiar place. This resolves the majority of hard geo-blocks, and it is among the most practical daily reasons travellers run a VPN at all, ahead of the security theatre. Two practicalities: pick a provider with solid server coverage in your home country specifically, and connect to the same city consistently, because a login from your home country is good and a login that teleports between cities daily is not. Our travel VPN ranking weighs home-country coverage for exactly this reason.
One caution worth stating: banks’ terms rarely prohibit VPN use, but their fraud models can also flag known data-centre IP ranges. In our own check the login sailed straight through, and minutes later an “unusual activity” security email landed: the paper trail that precedes a freeze. If a login fails, or that email arrives, switch to plain mobile data before assuming lockout; between the two paths, one nearly always works.
Fix two: the SMS code problem, solved with dual SIM
The sneakier failure: the login works, then the bank sends a verification code to your home number, which sits in a drawer at home inside a physical SIM. This one has a clean solution. Install your travel data as an eSIM and keep your home SIM active in the phone alongside it, with data roaming off for the home line. Texts arrive on the home number free or nearly free in most destinations; your data flows through the travel eSIM; both live in one phone. This dual-SIM arrangement is the standard setup we describe in the iPhone install guide, and the receive-codes-while-abroad case is the single best argument for it.
Longer term, move what your bank allows to app-based confirmation instead of SMS: app confirmations ride data, work anywhere, and are more secure anyway.
Fix three: preventing the card freeze
Login access is half the problem; the other half is the card itself getting declined or frozen after its first foreign transaction; the two-minute triage covers that queue moment. The prevention list is short: set a travel notice in the app where your bank still offers one, make the first foreign transaction a small one rather than a hotel bill, and carry a second card from a different bank on a different network (the two-card system), kept in different luggage. Travel-first cards from the fintech generation, built for exactly this, are their own topic over in our travel money hub.
The before-you-fly banking checklist
| Do at home | Prevents |
|---|---|
| Log into the bank through the VPN once | First-contact flags happening abroad |
| Confirm your home SIM stays active for SMS | The vanished-verification-code trap |
| Switch 2FA to app-based where offered | SMS dependence entirely |
| Set travel notices; note the fraud-line number | The freeze, and the hour on hold after it |
| Arrange a backup card, different bank + network | Single point of failure at a foreign ATM |
Do those five and the bank problem mostly stops existing. A sixth habit costs nothing while you are at it: refuse any terminal’s offer to charge your home currency, because the DCC trap quietly takes 3-8% per press. On the road, the remaining rule is situational: do banking on mobile data or through the VPN, never on raw hotel or airport wifi, for the reasons the hotel wifi threat model lays out.
Already locked out abroad? The recovery ladder
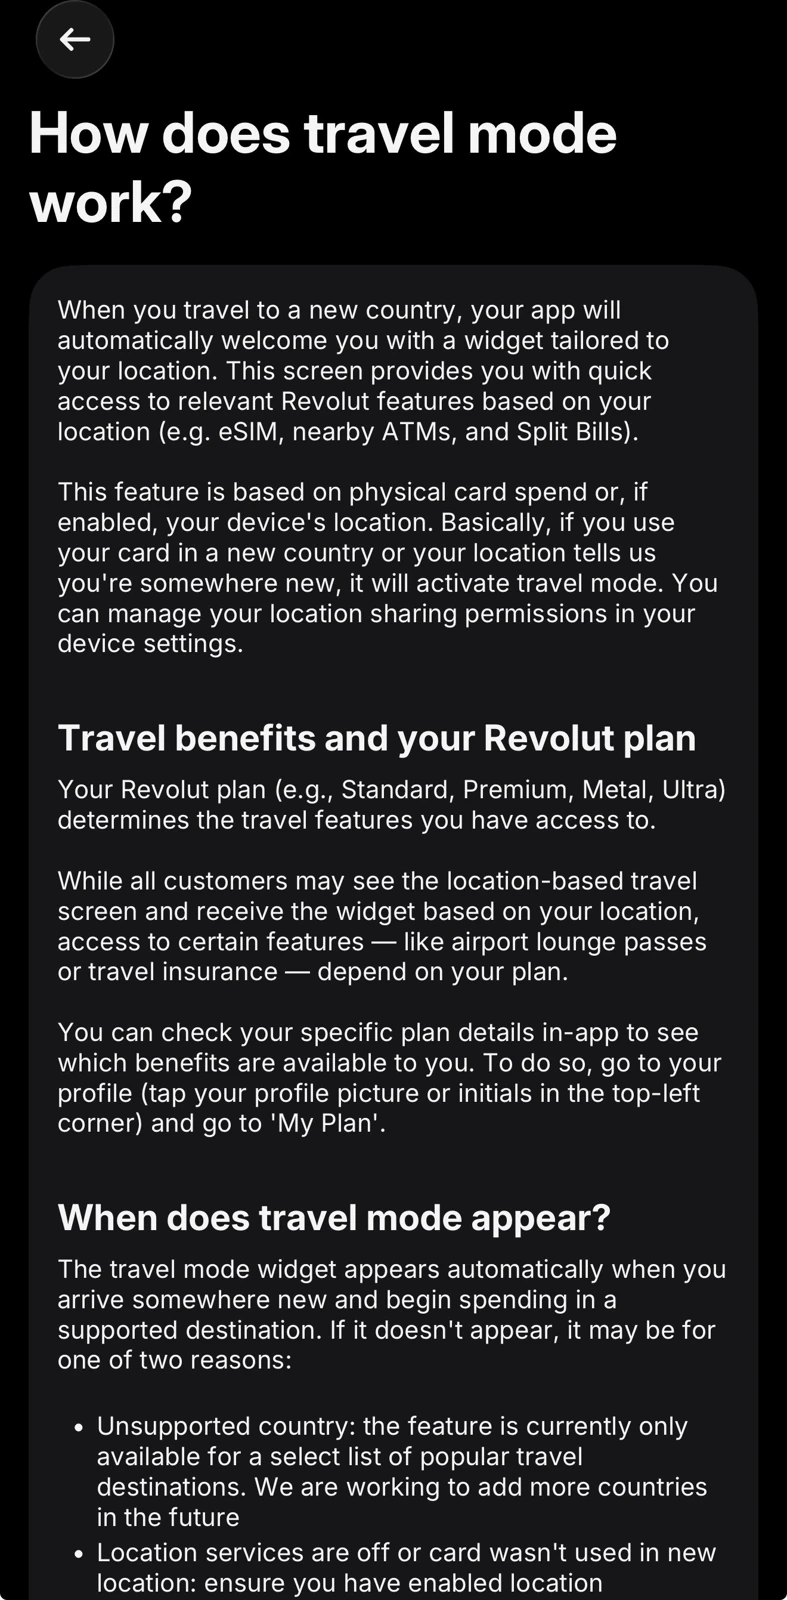
If you are reading this from a hotel with a frozen login, work the ladder in order. First, the cheap wins: try the login on plain mobile data if you were on wifi, or through the VPN’s home-country server if you were direct; between those paths one usually clears the geo-flag. Second, the app rather than the website, or the reverse: banks’ fraud rules often differ between the two front doors, and the other one may still be open. The sequence with the best reported hit rate against VPN-hostile banks: clear the browser cache, connect to a home-country server, log in via the browser first rather than the app, complete the 2FA there, and only then try the app.
Third, self-service unlock: many banks’ “verify it’s you” flows work from abroad if you can receive the code, which is where the home-SIM-active arrangement pays for itself retroactively. No SMS access is the hard wall; some banks will move verification to email or in-app approval if you can reach any logged-in session on another device, which is a strong argument for not logging out of the tablet that stayed in the hotel safe.
Fourth, the phone call, with the fraud line number you saved and the patience you did not: call centres can verify identity by other means and lift flags on the spot. If the card itself is frozen rather than the login, this is usually the only rung that works. And afterwards, do the five-item checklist above for the next trip, because every rung of this ladder is more pleasant at home than it was just now.
FAQ
Why did my bank block my login from abroad?
Because a first login from a new country looks exactly like credential theft, so the fraud model flinches. Approve the in-app prompt and retry, or log in through a VPN server at home so the login looks local, which is the quiet reason a VPN belongs in the banking toolkit.
Should I tell my bank I’m traveling?
App-first banks do not need it; they read context from the app itself. Legacy banks still run travel-notice systems, and one saved phone call abroad repays the two minutes it takes.
Is SMS 2FA a problem abroad?
The classic trap: codes sent to a home number you cannot receive. Keep the home SIM active for texts while an eSIM does the data, or better, move 2FA into an authenticator app before flying. Ideally both.